
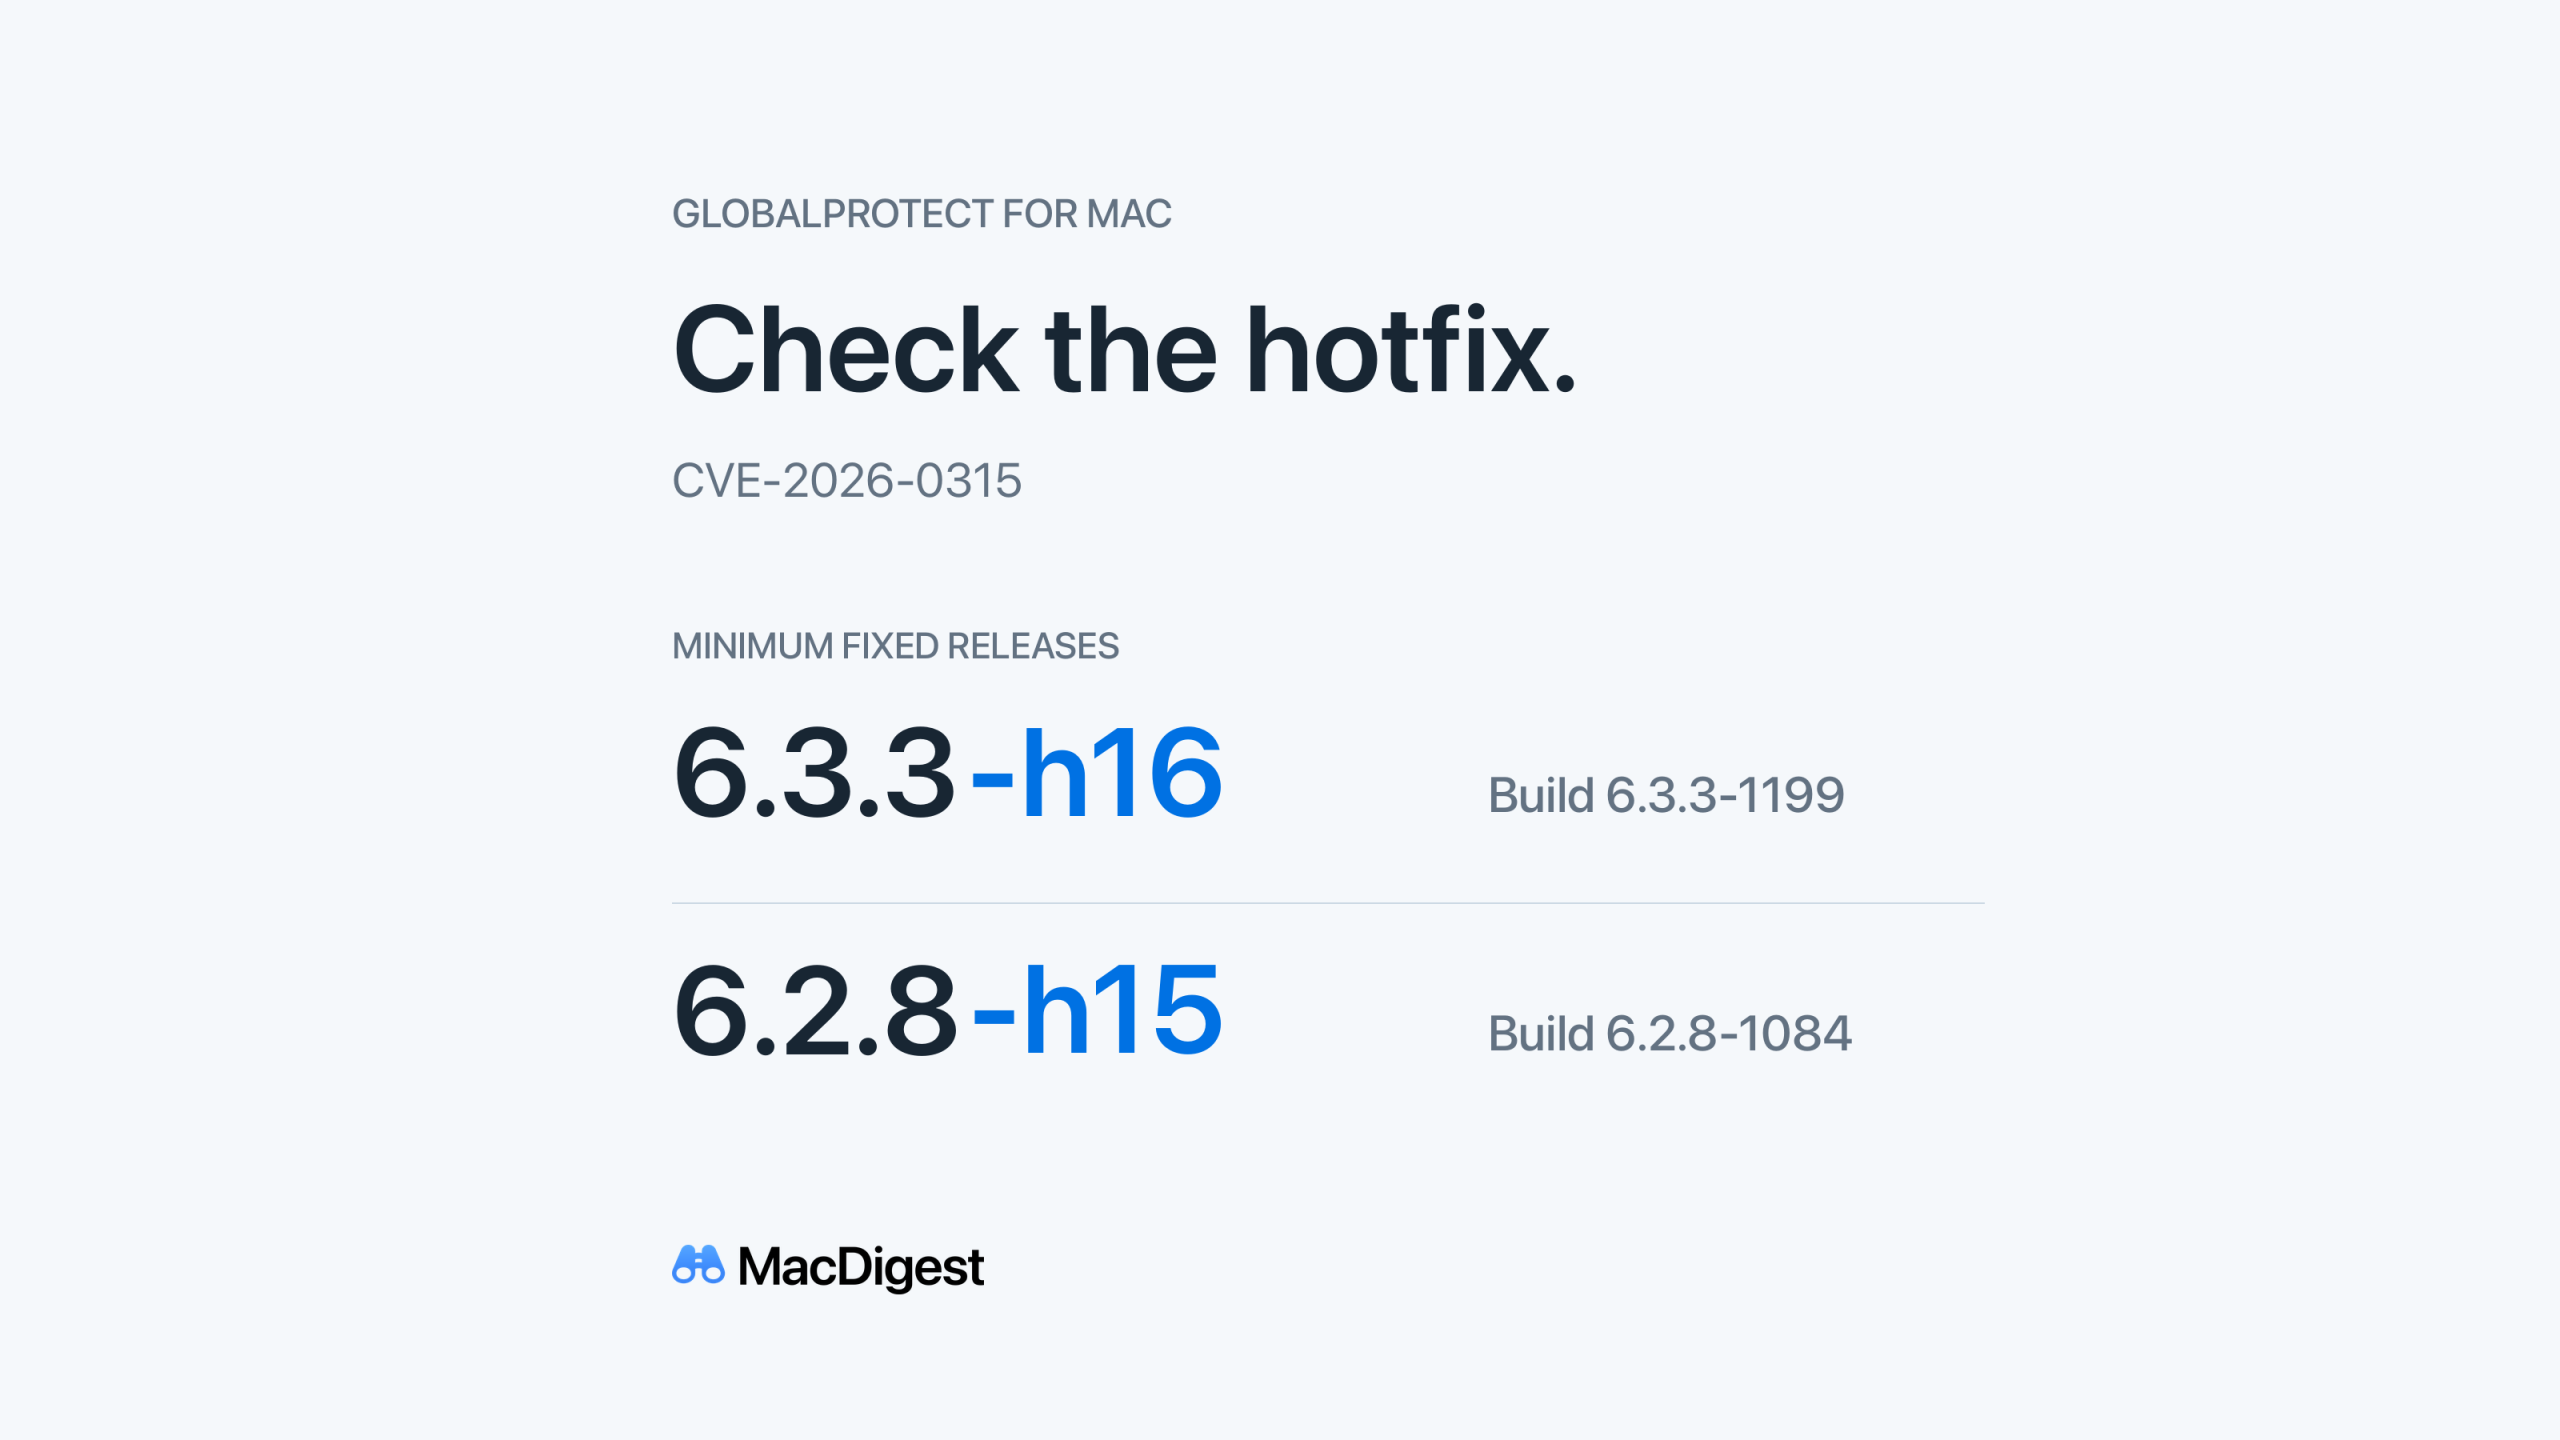
Check the full hotfix and build number against the vendor’s branch-specific fixes. Illustration: MacDigest.
GlobalProtect users on managed Macs should check their installed hotfix with IT. Palo Alto Networks’ October 14 advisory for CVE-2026-0315 identifies a flaw that lets a local, low-privilege user gain root access.
Check the full version
The advisory lists these minimum fixed releases for the two macOS branches:
| Branch | Minimum fixed hotfix | Build |
|---|---|---|
| 6.3 | 6.3.3-h16 | 6.3.3-1199 |
| 6.2 | 6.2.8-h15 | 6.2.8-1084 |
Earlier versions within each branch are affected. A version label of “6.3.3” or “6.2.8” alone is insufficient: check the hotfix suffix or full build. The advisory does not list macOS branches 6.0 or 6.1, so their omission should not be read as confirmation of safety.
A local escalation risk
Exploitation requires local access with low privileges and needs no special configuration. Root access allows commands to run with administrative privileges. Palo Alto Networks rates the issue medium, with a 5.9 CVSS-BT score and moderate urgency. As of its October 14 advisory, the company says it knows of no malicious exploitation and offers no workaround.
Linux, Windows, iOS, Android and ChromeOS are explicitly unaffected by this CVE.
Coordinate the update with IT
For GlobalProtect 6.3, the vendor’s macOS user guide places the installed version in Settings → About. Record the full version and ask IT to confirm which approved package includes the fix. The correct release depends on the organization’s environment; Palo Alto Networks does not provide a universal direct download.
For administrators, compare endpoint inventory against the branch-specific minimums, schedule deployment through the usual managed channel, and verify the installed build afterward. Test normal access to required work resources before closing the rollout.
Keep the organization’s VPN protections in place while arranging the update. Treat this as a coordinated patching task; downloading an unfamiliar installer or changing network controls can create a separate problem.